
Handling the information you entrust to us with care
ISO 27001 software developer
Would you like to have software built and be able to substantiate why you trust your developer? APPelit is ISO 27001-certified. We build and improve applications based on your functional wishes and agreed security requirements. This gives information security a concrete place in your development assignment.
- 01ISO 27001
- 02Access rights
- 03Logging
- 04Tested use
Who builds your software?
A development partner that can substantiate its approach
Your employees want to be able to consult customer data, customers expect access to their own documents, and suppliers need to be able to supply information. But not everyone should be able to see or change the same things. How do you want to arrange that access? Which data needs to be exchanged between systems? And what do you need to be able to trace back when a change has been made?
Working together with your developer also requires clarity. Which project information do you share, what access is needed, and how do we agree to handle this? Your organisation determines the desired functioning and content requirements; APPelit handles the technical implementation. We record which functionalities and security measures are part of the assignment and what the delivered components are tested against.
Collaboration
Your course, our craft
You know your organisation, your processes and your users best. That is why you make the functional choices, and we make sure the technology fits them seamlessly. We are happy to think along, while you stay in charge.
Where you set the direction
- Your business strategy and how IT supports it
- Standard software or custom build: what fits best
- Package choices and how your processes map onto them
- The functional requirements for the custom build
- Which data needs to move to the new system
- Rollout and training of your users
Where we deliver the technology
- Technical specification of the custom build
- Software development
- Testing and quality assurance (QA)
- Software security
- Technical execution of the data conversion
- Hosting and monitoring
Clear roles, one shared result
Security in practice
Your requirements translated into concrete software functions
Step 1
Access control
Should a customer only be able to open their own documents? Then we check not only which screens they see, but also requests for other data.
Step 2
Recording actions
If you want to be able to see changes afterwards, we record which user carried out an agreed action and when.
Step 3
Logging in and integrations
Extra login verification or restrictions on data exchange via integrations can be part of the development.
Step 4
Testing
Every agreed requirement is given a technical elaboration, with tests on both permitted and non-permitted use.
What is tested?
The meaning and limits of our certification
ISO 27001 is the international standard for an information security management system, also known as an ISMS. In it, an organisation sets out how it manages information risks, allocates responsibilities and continues to assess and improve its measures. An independent certifying body assesses whether the management system complies with the standard, within the activities covered by the certificate. The certificate does not automatically make your app or business software ISO 27001-certified and is no guarantee that vulnerabilities will never occur. That is why your project-specific requirements and the technical implementation remain important.
Case study
Ease of use and controlled access
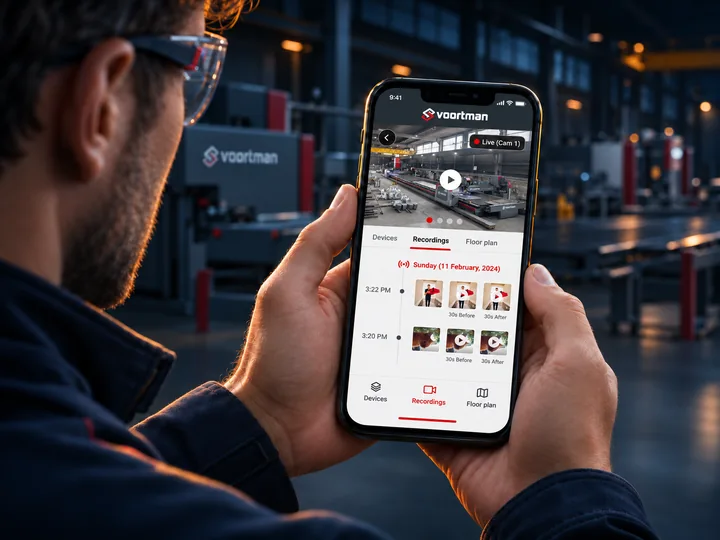
Voortman
Mobile app for Android and iOS
APPelit built a mobile application that allows authorised users to consult operational information and carry out actions. Access rights and the connection with underlying systems were taken into account.
View the caseRead more
Frequently asked questions about ISO 27001
What is ISO 27001?
The international standard for an information security management system (ISMS). An organisation sets out in it how it manages information risks, divides responsibilities and continues to assess and improve its measures.
Is my app ISO 27001 certified if APPelit builds it?
No. The certificate does not automatically make your app or business software ISO 27001 certified and is not a guarantee that vulnerabilities will never occur. Your project-specific requirements and the technical execution remain important.
How do I check APPelit's certification?
Via the Our certificates page, you can request the current certificate after an introductory meeting. It states the certificate holder, standard version, validity and scope.
Is maintenance and updates included?
We record technical maintenance, updates and the monitoring of vulnerabilities separately. This way, you know what APPelit develops and which work is included.
Contact
Discuss your project?
Leave your details. Within 24 hours, a specialist will contact you for an introductory meeting.