Software assurance
Software assurance: quality and continuity
How important is your software for daily operations? When an application becomes business-critical, you don't just want new features built. Testing, security, availability and continuity also deserve attention. With software assurance, APPelit carries out concrete technical activities to support these aspects.
- 01Testing
- 02Security
- 03Cloud
- 04Software escrow
What do you want to safeguard?
Agreements regarding your software
Do customers always need access to important data? Would you like to know whether a new release works properly before it goes live? Or would you like to limit dependency on a single software supplier? Not every application needs the same measures.
Perhaps your priority lies with more extensive testing, with security, or with hosting and availability. You determine which requirements apply to your organisation. We carry out the agreed technical work and make clear what does and does not fall within the assignment.

Collaboration
Your course, our craft
You know your organisation, your processes and your users best. That is why you make the functional choices, and we make sure the technology fits them seamlessly. We are happy to think along, while you stay in charge.
Where you set the direction
- Your business strategy and how IT supports it
- Standard software or custom build: what fits best
- Package choices and how your processes map onto them
- The functional requirements for the custom build
- Which data needs to move to the new system
- Rollout and training of your users
Where we deliver the technology
- Technical specification of the custom build
- Software development
- Testing and quality assurance (QA)
- Software security
- Technical execution of the data conversion
- Hosting and monitoring
Clear roles, one shared result
Certainty in layers
Testing, security, cloud and escrow
- 01
Cybersecurity and pentesting
Carrying out security measures and specifically investigating possible vulnerabilities within the scope.
- 02
Cloud computing
Technical setup of hosting, scalability and availability.
- 03
Software escrow
Additional assurance regarding access to the source code when a supplier can no longer deliver.
Approach
Targeted research and support
Step 1
Determining requirements
You determine which requirements apply regarding availability, security, quality and continuity.
Step 2
Choosing components
We combine the components that suit your software and requirements.
Step 3
Defining scope
In advance, we record what will be tested or carried out, in which environments and with which deliverables.
Step 4
Carrying out and reporting
We carry out the work. Follow-up adjustments are agreed separately.
Honest about security
No guarantee, but concrete measures
Software assurance does not mean that software is guaranteed to never contain errors, never fail or never be vulnerable. It is about concrete measures that allow you to better investigate, limit or manage technical risks. A penetration test has a different scope than functional testing, and software escrow a different purpose than cloud hosting. This keeps it clear what is being investigated, what is being adjusted and what support is needed afterwards.
Case study
First insight into code and cloud
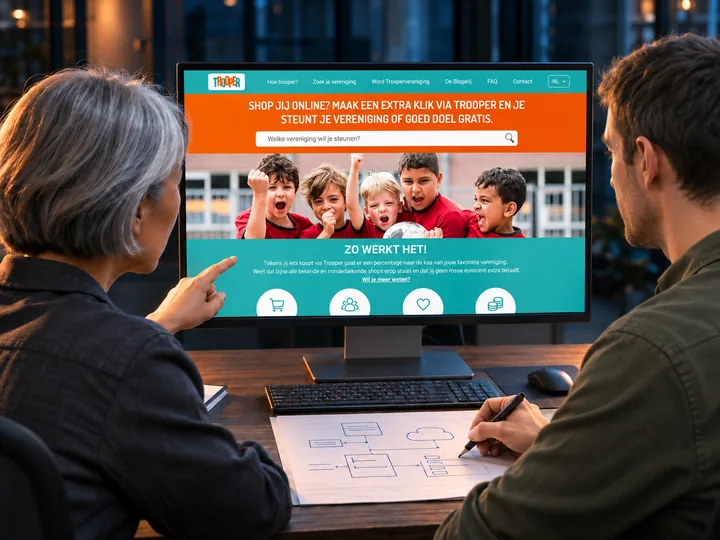
Trooper
Assessment of code and Azure configuration
APPelit assessed both the code and the Azure configuration before further development was considered.
View the caseRead more
Frequently asked questions about software assurance
What is software assurance?
A combination of technical activities that support the quality, security and continuity of your software, such as software testing, cybersecurity, penetration testing, cloud solutions and software escrow.
Does software assurance guarantee that my software is error-free?
No. It concerns concrete measures that allow you to better investigate, limit or manage technical risks. In advance, we record what will be tested or carried out.
What is the difference between a pentest and software testing?
Functional testing checks whether agreed functionalities work. A penetration test specifically investigates possible technical vulnerabilities within the agreed scope.
When is software escrow useful?
When your organisation is heavily dependent on a single supplier and you want certainty about access to the source code if that supplier is no longer able to deliver.
Information security
Secure by design. Demonstrably.
Do you work with personal or healthcare data? Then you want to be sure that your software partner handles information carefully. APPelit is ISO 27001- and NEN 7510-certified.
ISO 27001
The international standard for information security. Risks, access and incidents are recorded in a management system that is periodically assessed.
NEN 7510
The Dutch standard for information security in healthcare. Important when your software works with medical or health data.
- Security requirements included from the very first specification
- Test cases that align with recorded security requirements
- AI functions also fall within the same data agreements
Contact
Would you like more grip on your software?
Leave your details. Within 24 hours, a specialist will contact you for an introductory meeting.