
Information security in software development
ISO 27001 / NEN 7510
Does your software work with confidential business information, personal data or healthcare data? Then you're looking for a developer who handles this carefully. APPelit is ISO 27001- and NEN 7510-certified. This way, you can factor our approach to information security into your choice of development partner.
- 01ISO 27001
- 02NEN 7510
- 03Security requirements
- 04Certificates available on request
What is important to you?
Your information, your principles
Who may view which data? What information may your application exchange? And which actions do you want to be able to trace afterwards? You want employees to be able to work pleasantly, without confidential information being accessible to everyone. In addition, your organisation may have specific requirements for the parties working on your software.
Whether you are extending existing software or having a new application built: your organisation determines the desired functionalities and content requirements. APPelit handles the technical elaboration and build. We make concrete agreements about what we develop, which security measures apply, and how we test the agreed functioning.
Collaboration
Your course, our craft
You know your organisation, your processes and your users best. That is why you make the functional choices, and we make sure the technology fits them seamlessly. We are happy to think along, while you stay in charge.
Where you set the direction
- Your business strategy and how IT supports it
- Standard software or custom build: what fits best
- Package choices and how your processes map onto them
- The functional requirements for the custom build
- Which data needs to move to the new system
- Rollout and training of your users
Where we deliver the technology
- Technical specification of the custom build
- Software development
- Testing and quality assurance (QA)
- Software security
- Technical execution of the data conversion
- Hosting and monitoring
Clear roles, one shared result
More information
Choose the topic that suits your question
- 01
ISO 27001
Looking to have software built by an ISO 27001-certified developer: what the standard assesses and how your requirements are reflected in the software.
- 02
NEN 7510
Have healthcare software, portals and integrations built by a NEN 7510-certified developer.
- 03
Our certificates
After an introductory meeting, you can request our certificates for your supplier assessment or internal review.
From requirements to software
Security receives a concrete elaboration
Step 1
Access rights
Rights per user role, so employees only see and change what belongs to their task.
Step 2
Log in
Where your requirements call for it: extra verification at login.
Step 3
Recording changes
Recording agreed actions, so you can review changes afterwards.
Step 4
Integrations
Restrictions on which data another system may request or modify.
What does certification say?
Justification for your choice of supplier
ISO 27001 sets requirements for the way an organisation organises, manages and improves information security. NEN 7510 focuses specifically on information security in healthcare and the handling of personal health information. During certification, an independent body assesses the management system within the defined scope. It is therefore not a separate quality mark for every application that is built. Project-specific requirements and agreements remain necessary for your software. That is why we specify exactly which technical measures are part of the development and which activities, such as maintenance and updates, are agreed separately.
Case study
Further developing existing healthcare software
LPZC
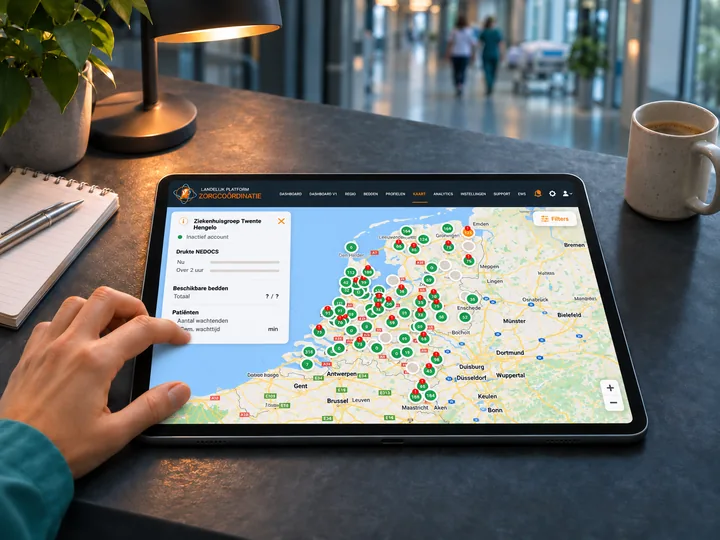
Software for insight into hospital capacity
APPelit contributed to expanding, improving and maintaining existing software that provides insight into hospital capacity and pressure in emergency care.
View the caseRead more
Frequently asked questions about ISO 27001 and NEN 7510
Is APPelit ISO 27001 and NEN 7510 certified?
Yes. APPelit is ISO 27001 and NEN 7510 certified. After an introductory meeting, you can request the certificates for your supplier assessment.
Will my software also be certified as a result?
No. During certification, an independent body assesses the management system within the established scope. It is not a separate quality mark for every application that is built. For your software, we make project-specific arrangements.
What is the difference between ISO 27001 and NEN 7510?
ISO 27001 sets requirements for the way an organisation organises, manages and improves information security. NEN 7510 focuses specifically on information security in healthcare and the handling of personal health information.
Who determines the security requirements for my software?
Your organisation determines the desired functionalities and content requirements. APPelit provides the technical development and build, and records which security measures belong to the assignment and how we test the agreed operation.
Contact
What do you want to build?
Leave your details. Within 24 hours, a specialist will contact you for an introductory meeting.