Software audit
Software audit: first insight, then build further
Do you want to expand your software but are unsure about the technical foundation? A software audit provides insight into the code examined, maintainability and technical points of attention. APPelit assesses the agreed components and documents the findings, so you can better substantiate your next development step.
- 01Code quality
- 02Maintainability
- 03Report
- 04ISO 27001 · NEN 7510
Can your software keep up?
Clarity before further development
Are adjustments taking longer and longer? Do the same errors keep returning? Or do you get different answers to the question of whether your software is still suitable for further development? Then you want to know first which components require attention, before investing time and budget again.
Your questions determine which components we include. You determine what the software should support for your organisation; we assess the examined components on the basis of the supplied requirements and agreed technical criteria.

Collaboration
Your course, our craft
You know your organisation, your processes and your users best. That is why you make the functional choices, and we make sure the technology fits them seamlessly. We are happy to think along, while you stay in charge.
Where you set the direction
- Your business strategy and how IT supports it
- Standard software or custom build: what fits best
- Package choices and how your processes map onto them
- The functional requirements for the custom build
- Which data needs to move to the new system
- Rollout and training of your users
Where we deliver the technology
- Technical specification of the custom build
- Software development
- Testing and quality assurance (QA)
- Software security
- Technical execution of the data conversion
- Hosting and monitoring
Clear roles, one shared result
What do we check?
Code, tests and technical setup
- 01
Readability and complexity
How understandable is the code and are components unnecessarily duplicated?
- 02
Tests
Which tests are present and how are they organised?
- 03
Documentation
Is enough documented to continue working with another team?
- 04
Security components
Technical security aspects within the agreed scope.
Approach
From question to findings
Step 1
Determining scope
We record which checks are carried out and which questions the audit should answer.
Step 2
Arranging access
You make the source code, documentation and, where agreed, a test or hosting environment available.
Step 3
Assess
We assess the agreed components. If access is missing, we make clear what has not been assessed.
Step 4
Report
You receive a report with findings and possible technical next steps.
What does it deliver?
Findings for your next decision
With the report, you can substantiate decisions about maintenance, adjustments or further development. We distinguish between established points of attention and questions that require additional investigation. You determine which work is given priority. The audit is not a guarantee that all errors or vulnerabilities will be found; adjusting software is a separate assignment.
Case study
Audit before scaling up
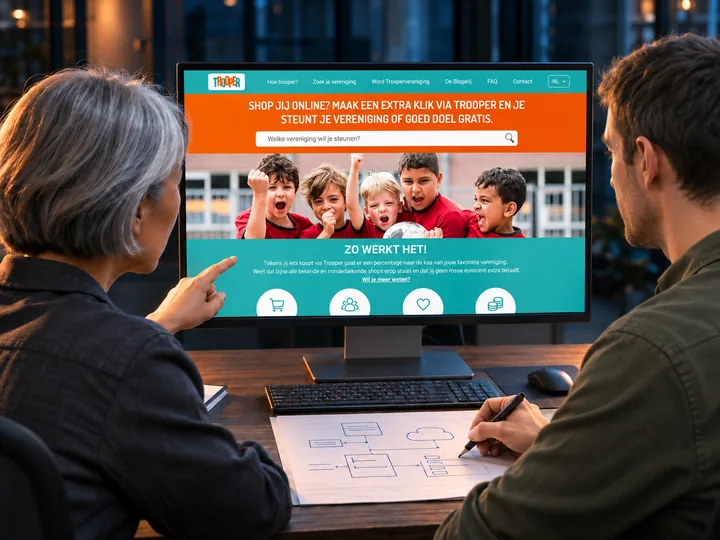
Trooper
Audit of code and Azure configuration
Before scaling up further, Trooper wanted to know the technical status of the application. APPelit assessed code quality, software versions and security.
View the caseRead more
Frequently asked questions about a software audit
What is a software audit?
A technical assessment of agreed parts of your software, such as code, tests, documentation and security components. The findings are recorded in a report.
What does APPelit need for an audit?
Appropriate access to the source code, relevant documentation and, where agreed, a test or hosting environment. The requirements for the current software and planned extensions are also useful input.
Does an audit find all errors?
No. An audit is not a guarantee that all errors or vulnerabilities will be found. We limit the assessment to the agreed components and make clear where it ends.
Does APPelit also resolve the identified issues?
That is possible, as a follow-up assignment. Repair or further development is not automatically included in the audit. You determine which work takes priority.
Information security
Secure by design. Demonstrably.
Do you work with personal or healthcare data? Then you want to be sure that your software partner handles information carefully. APPelit is ISO 27001- and NEN 7510-certified.
ISO 27001
The international standard for information security. Risks, access and incidents are recorded in a management system that is periodically assessed.
NEN 7510
The Dutch standard for information security in healthcare. Important when your software works with medical or health data.
- Security requirements included from the very first specification
- Test cases that align with recorded security requirements
- AI functions also fall within the same data agreements
Contact
Do you want to know how your software is doing?
Leave your details. Within 24 hours, a specialist will contact you for an introductory meeting.